
Supporting technical study
Google Cloud VPC & Load Balancing Lab
Built a temporary Google Cloud VPC, tested how firewall rules change VM reachability, and distributed HTTP requests across three web servers.
Completed
Completed October 2026
Google Cloud · Compute Engine · VPC firewall · Cloud Shell · gcloud CLI · Network load balancing
The problem
A cloud network needs deliberate rules for which machines can communicate, while a public web endpoint needs a way to spread traffic across multiple servers.
My contribution
- Configured virtual machines, VPC firewall rules, and a network load balancer in a temporary Google Cloud lab.
- Ran connectivity and HTTP checks, then preserved terminal captures and removed the lab resources.
Evidence you can inspect
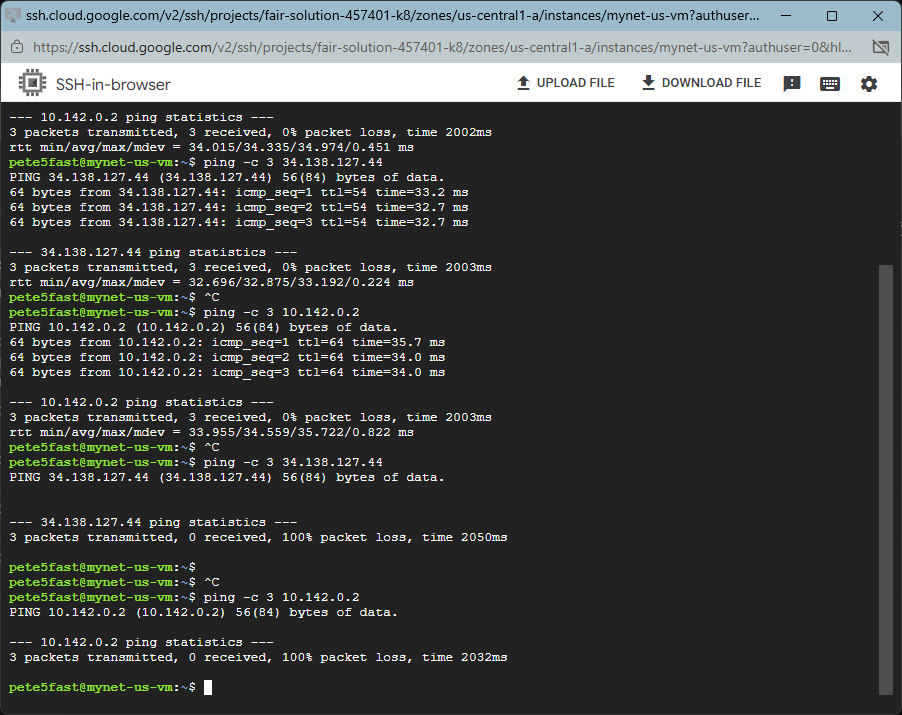
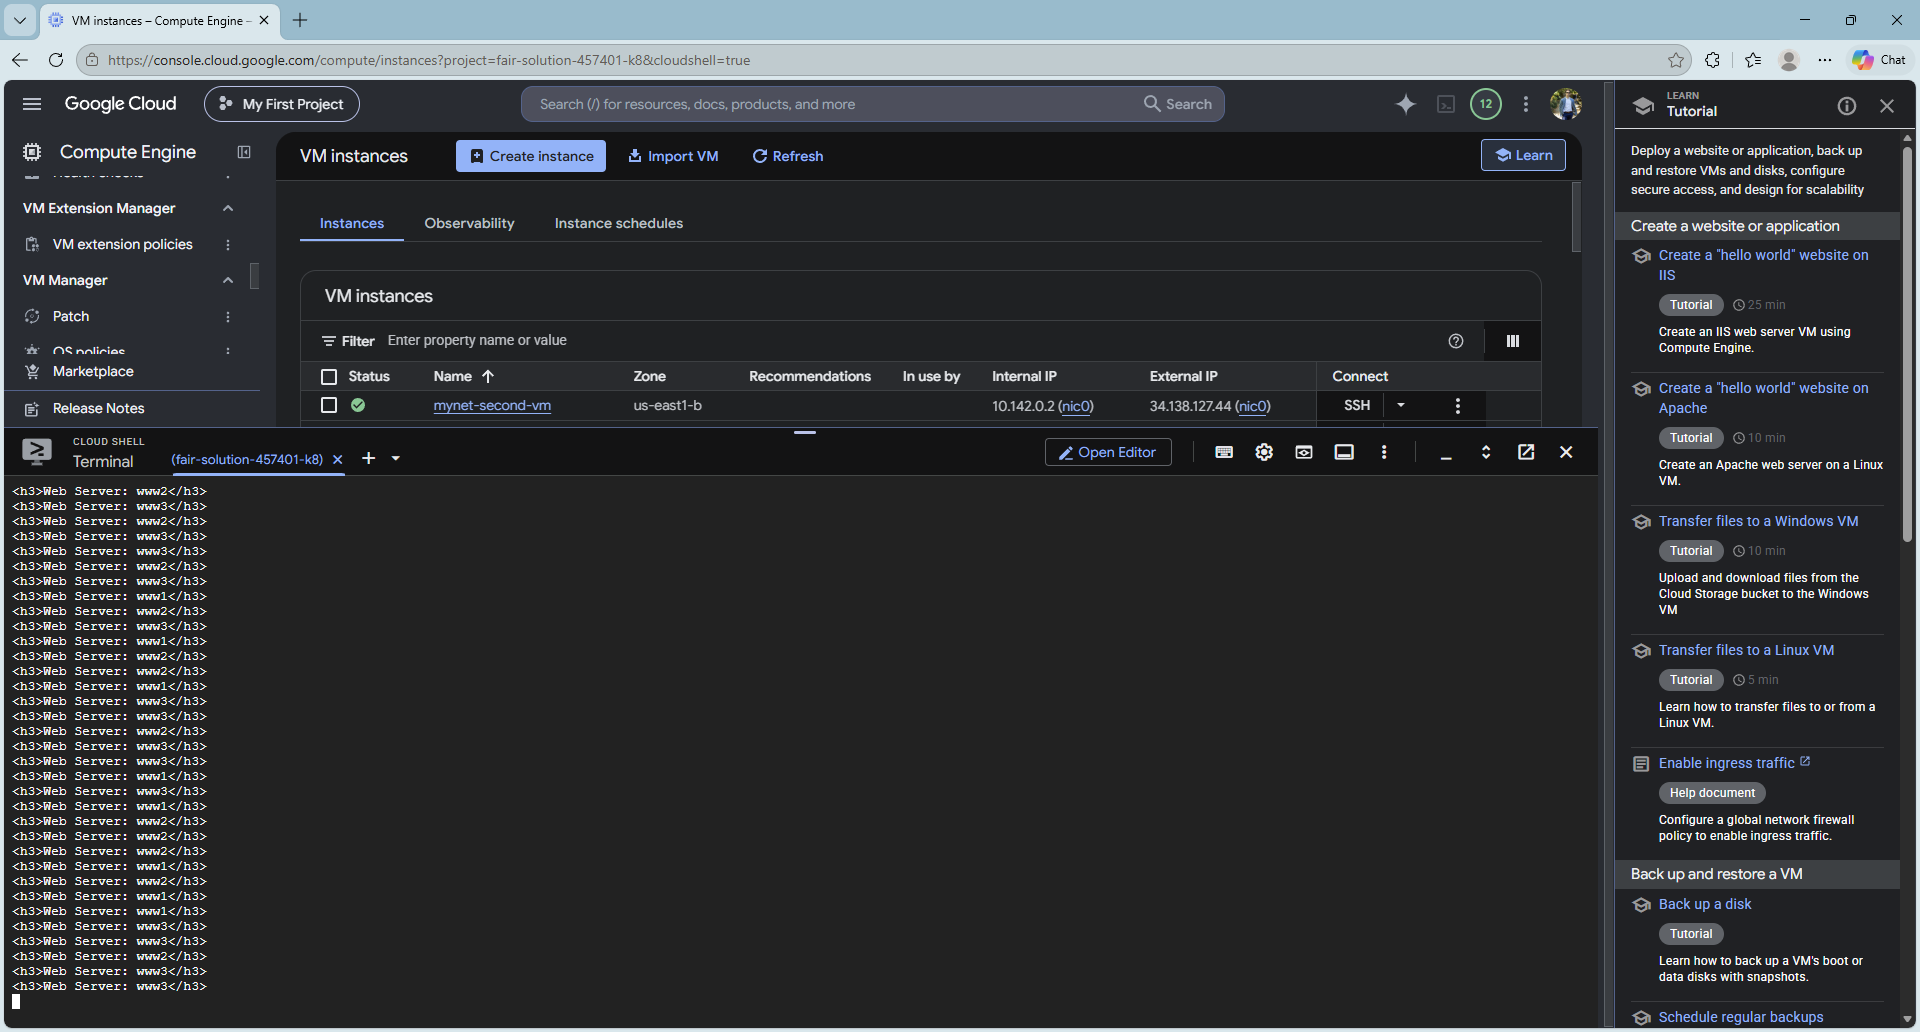
The screenshots preserve two observations from the temporary lab: changed reachability after firewall-rule removal and HTTP responses identifying each of three backends.
Three web servers behind one endpoint
Recorded observations
- Initial internal and external pings: 3 of 3 responses each
- After removing the ICMP rule: external ping lost 3 of 3 packets; internal ping still received 3 of 3
- After removing the internal custom rule: internal ping lost 3 of 3 packets
- Repeated HTTP requests returned responses labeled www1, www2, and www3
- Temporary lab resources were deleted after testing; this is coursework, not a live production service
How I approached the work
- Created a VPC and VMs in us-central1 and us-east1, then verified 3 of 3 ping responses to the second VM's internal and external addresses.
- Deleted the ICMP allow rule; the external ping lost all three packets while the internal ping still worked.
- Deleted the internal custom allow rule; the internal ping then lost all three packets.
- Created three Apache VMs, a health check, target pool, reserved IP, and forwarding rule; repeated curl requests returned www1, www2, and www3.
- Removed the temporary load balancer, servers, firewall rules, VMs, and VPC after testing.
Demonstrated outcomes
- Ping behavior changed when ingress rules were removed.
- Repeated HTTP requests returned responses from www1, www2, and www3.
Limitations and unfinished work
- This is academic lab evidence, not production infrastructure or a cloud certification.
- The temporary resources were deleted. The captures do not establish load capacity, uptime, or performance under traffic.
Explore further
- Inspect firewall test output
Open the original public terminal capture of connectivity before and after firewall changes.
- Inspect three backend responses
Open the public capture identifying responses from the three web servers.
- Read the lab note
Read the accompanying public account of the test sequence.